What do high-compliance regulated software testing services cover?
High-compliance testing services incorporate a full suite of functional and non-functional testing disciplines designed to satisfy external audit standards.
These services encompass regulatory requirement validation, vulnerability assessment, load and performance stress testing, and system integration verification. Every phase is executed using structured methodologies that generate the exact documentation required by inspectors.
The key to success lies in the vendor’s ability to maintain a clear requirement traceability matrix from day one. This rigorous approach **prevents compliance discrepancies between design specifications and deployed software**.
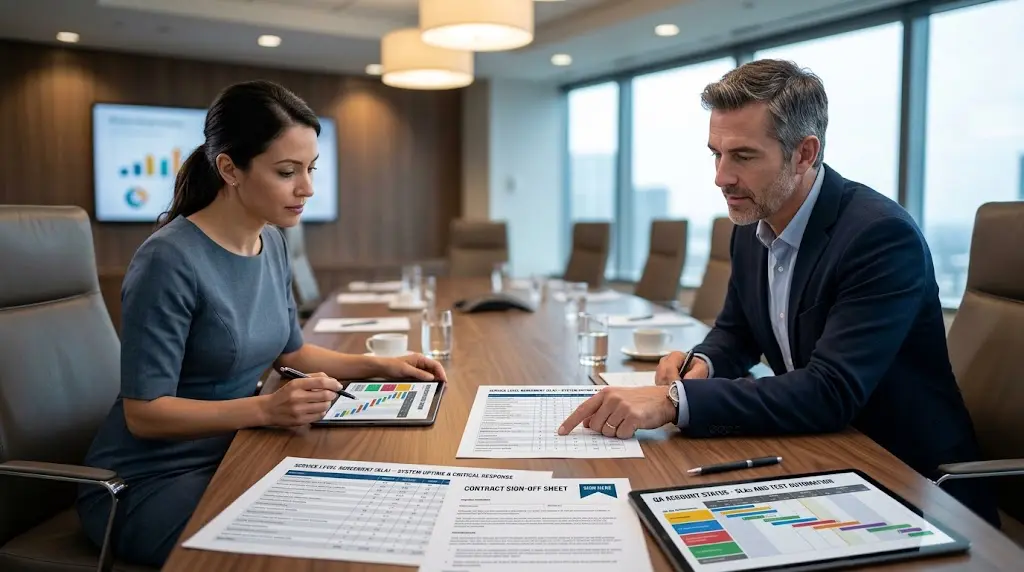
How to structure Service Level Agreements (SLA) for QA compliance audits?
Defining clear key performance indicators (KPIs) in procurement contracts is essential for measuring service quality and accountability.
- Code coverage thresholds: Mandatory percentage benchmarks for automated test coverage across regulated business rules.
- Defect resolution response times: Strict timelines for identifying, logging, and re-testing high-severity security vulnerabilities.
- Audit deliverable requirements: Mandatory delivery of signed execution logs and compliance certificates following each test cycle.
These contractual terms align operational expectations between the enterprise and the QA vendor. A well-negotiated SLA protects software investments and establishes clear accountability.
Which engagement model best suits projects with strict regulatory needs?
Choosing between dedicated testing teams and project-based engagements depends on the continuity and complexity of your software release schedule.
Dedicated QA teams versus project-based testing
Dedicated testing teams integrated directly into the client’s development workflow accumulate deep domain knowledge regarding specific compliance rules. For continuous software development under agile frameworks, a dedicated team model delivers far greater efficiency than temporary project contracts.
This long-term integration allows organizations **to maintain continuous regulatory oversight across every software release**.
Why do regulated software testing services mitigate long-term legal risks?
Non-compliance with software regulations in audited sectors can trigger severe financial penalties and immediate loss of commercial licenses.
- Demonstrating due diligence to regulatory authorities through independent, third-party audit reports.
- Mitigating liability risks associated with data protection failures or software downtime.
- Protecting enterprise reputation and market standing among clients and industry partners.
Proactive quality assurance is always the most cost-effective strategy. By procuring specialized regulated software testing services, technology companies ensure compliance and build a secure foundation for long-term growth.